Fingerprinting and Mapping UAC‑0099 Infrastructure
Discovering Identifiers From UAC-0099 Infrastructure To Build a Distinct Fingerprint
The infrastructure of the threat actor UAC-0099 was analyzed to uncover additional C2 servers and a revealing fingerprint of their MATCHBOIL C2. The group’s infrastructure was intended to be behind Cloudflare, but likely due to mistakes in setting up the C2 servers, they could still be identified.
In addition to identifying MATCHBOIL C2 servers, the analysis revealed other infrastructure associated with UAC-0099. The analysis also confirmed the findings ESET made about the way UAC-0099 sets up their infrastructure and revealed additional identifying infrastructure characteristics.
Key Findings
- UAC-0099 infrastructure is often set up in similar fashion, using nginx & Let’s Encrypt
- The group reuses the same domain registrars
- The ASN for the C2 servers has always been the same
- MATCHBOIL C2 responds in a very curious way, even to scanners such as Modat Magnify & FOFA
- UAC-0099 likes cats
Malware Campaign But With Cat Pics
UAC-0099 is a threat actor that has been active since at least 2022. The threat actor commonly targets Ukrainian targets. The first mentions of the group were by the Computer Emergency Response Team of Ukraine (CERT-UA). ESET characterizes the threat actor as Russia-aligned and as working as an initial access broker for Sandworm. Mandiant also connects UAC-0099 to APT44, which is also known as Sandworm. Sandworm is most well known for being attributed to the Russian military intelligence service GRU and targeting the Ukrainian electric grid with destructive attacks.
UAC-0099 has been known to deploy a downloader called MATCHBOIL. The group uses MATCHBOIL as a first-stage downloader to deliver a second-stage payload from a C2 server and install it on the victim’s system. MATCHBOIL is distributed by spearphishing emails, which often direct victims to execute a malicious file that is hosted on a file sharing site. MATCHBOIL has been around since at least 2024 and has seen new variants as recently as April 2026. MATCHBOIL, or its spreading mechanism, does not appear particularly interesting or advanced. The malware actually appears quite crude, using some less than convincing graphical user interfaces as forms of lures. But I have to admit, the cat pictures did pique my interest.
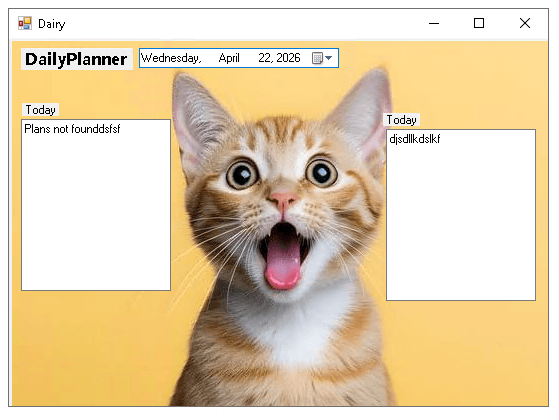 GUI shown to victim after running MATCHBOIL identified by ESET
MATCHBOIL Infrastructure
In their report ESET identifies two IP addresses and four domains used by UAC-0099 as MATCHBOIL C2 servers. They also note the threat actor uses VPS services, such as BitLaunch to host their C2 servers, Cloudflare to hide the C2 servers real IP addresses and Let’s Encrypt certificates for the C2 servers. It turns out, their infrastructure setup had left a bunch of clues that could be used to build a fingerprint.
| Indicator | Description | First seen |
| virtualdailyplanner[.]pro | MATCHBOIL C2 | 2025‑11‑10 |
| telemetry-conf[.]com | MATCHBOIL C2 | 2025‑08‑12 |
| flycloud-service[.]com | MATCHBOIL C2 | 2026‑03‑03 |
| airarticlegenerate[.]com | MATCHBOIL C2 | 2025‑05‑07 |
| 64.95.10[.]223 | MATCHBOIL C2, flycloud-service[.]com resolved here | 2026‑03‑03 |
| 64.95.13[.]210 | MATCHBOIL C2, airarticlegenerate[.]com resolved here | 2025‑05‑07 |
Domain Analysis
The domain analysis revealed some additional pivot points and a pattern. The pivot points were the real IP addresses behind telemetry-conf[.]com and virtualdailyplanner[.]pro, which ESET had not managed to identify. The IP addresses were identified from Validin’s DNS history data.
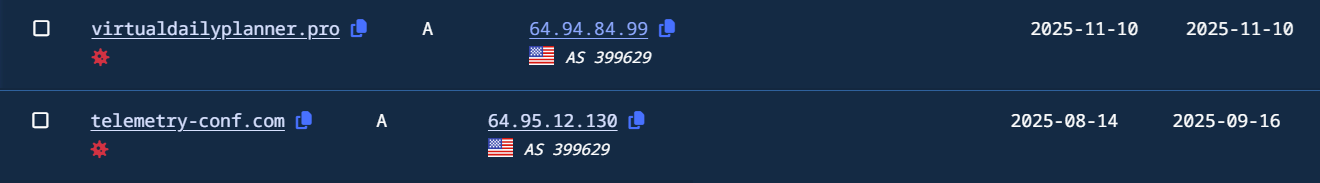 Real hosts behind malicious domains identified via Validin
Whois data for the domains revealed a clear pattern. While the registrant information for all of the domains was redacted by privacy features, the registrar used was the same for three of the four domains.
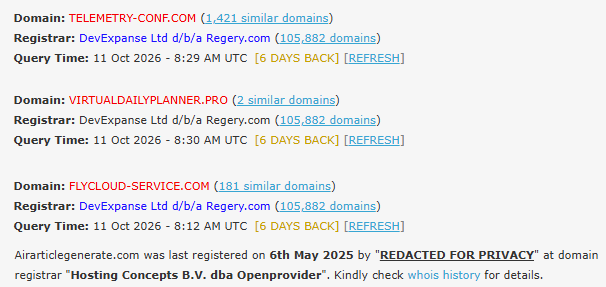 DevExpanse and Hosting Concepts registrars used by the threat actor.
Host Analysis
Because the infrastructure identified by ESET was already dated and only a few IP addresses were identified, my expectations for new findings were not high. However, the historical data did have some promising leads.
FOFA had successfully recorded the response from the likely C2 service for two of the IP addresses: 64.95.12[.]130 for telemetry-conf[.]com and 64.95.10[.]223 for flycloud-service[.]com. The services on these hosts did not initially appear very similar, for example they had a different nginx version and JARM hash. But some similarities could still be seen:
- ASN was the same: 399629
- The headers were the same, except the nginx version
- JA3s values were the same
- HTTP response body was similar
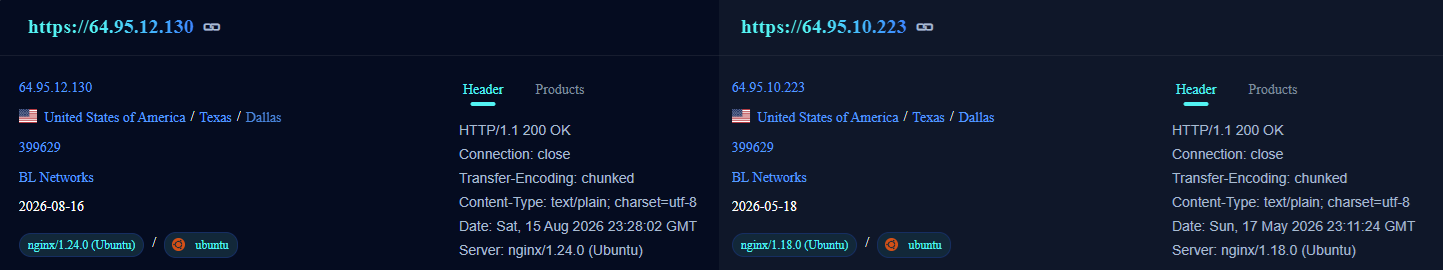 Similar HTTP headers for both hosts, except for the nginx version.
The HTTP response body proved to be the smoking gun: both services replied with a different, seemingly random, 10-character string that was highly suspicious and indicative of a C2 server. Turns out this 10-character string changes every time the C2 responds.
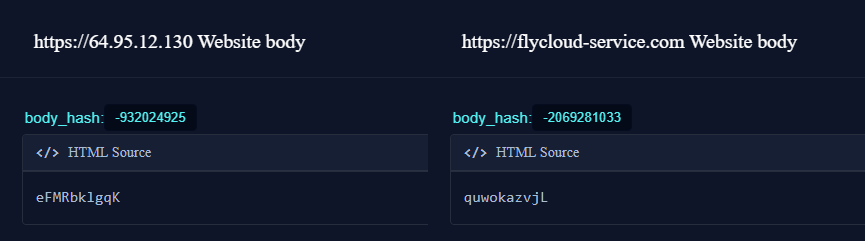 Reply from the C2 servers.
These identifiers were combined into a search query for FOFA that, at least currently, reveals only true positive findings: asn="399629" && header="Transfer-Encoding: chunked" && header="Content-Type: text/plain; charset=utf-8" && (header="Server: nginx/1.24.0 (Ubuntu)" || header="Server: nginx/1.18.0 (Ubuntu)") && header!="Cache-Control: no-store".
This query revealed a bunch of previously unidentified C2 servers:
| IP | Domain | First seen on FOFA |
| 192.153.57[.]148 | exchange-cab-center[.]com | 2026-09-16 |
| 64.94.85[.]94 | thunderbird-smp-extension[.]com | 2026-08-08 |
| 64.94.85[.]179 | api-available-checker[.]com | 2026-03-04 |
| 64.95.10[.]87 | gold-kauf-limited[.]bar | 2026-10-02 |
| 64.95.11[.]193 | industriesbetbikeupdate[.]com | 2026-09-30 |
| 64.94.84[.]227 | remote-fileviewer[.]com | 2026-06-18 |
| 64.95.13[.]135 | cloud-fileengine[.]com | 2026-06-28 |
| 64.95.10[.]235 | activation-planner[.]pro | 2026-04-06 |
These hosts all returned the similar 10-character string and identical headers, outside the nginx versions. This is already solid proof these are part of the C2 infrastructure for UAC-0099, almost certainly specifically for MATCHBOIL. As further confirmation, these newly identified domains were all registered with either DevExpanse or Hosting Concepts and the certificates used for the hosts were generated with Let’s Encrypt. Further matching the infrastructure identifiers seen by ESET.
Using Modat Magnify, and the historical visibility the platform provides, it was possible to identify one additional host that had been running the same C2 service: 64.95.12[.]170/cache-extension-api-tool[.]icu.
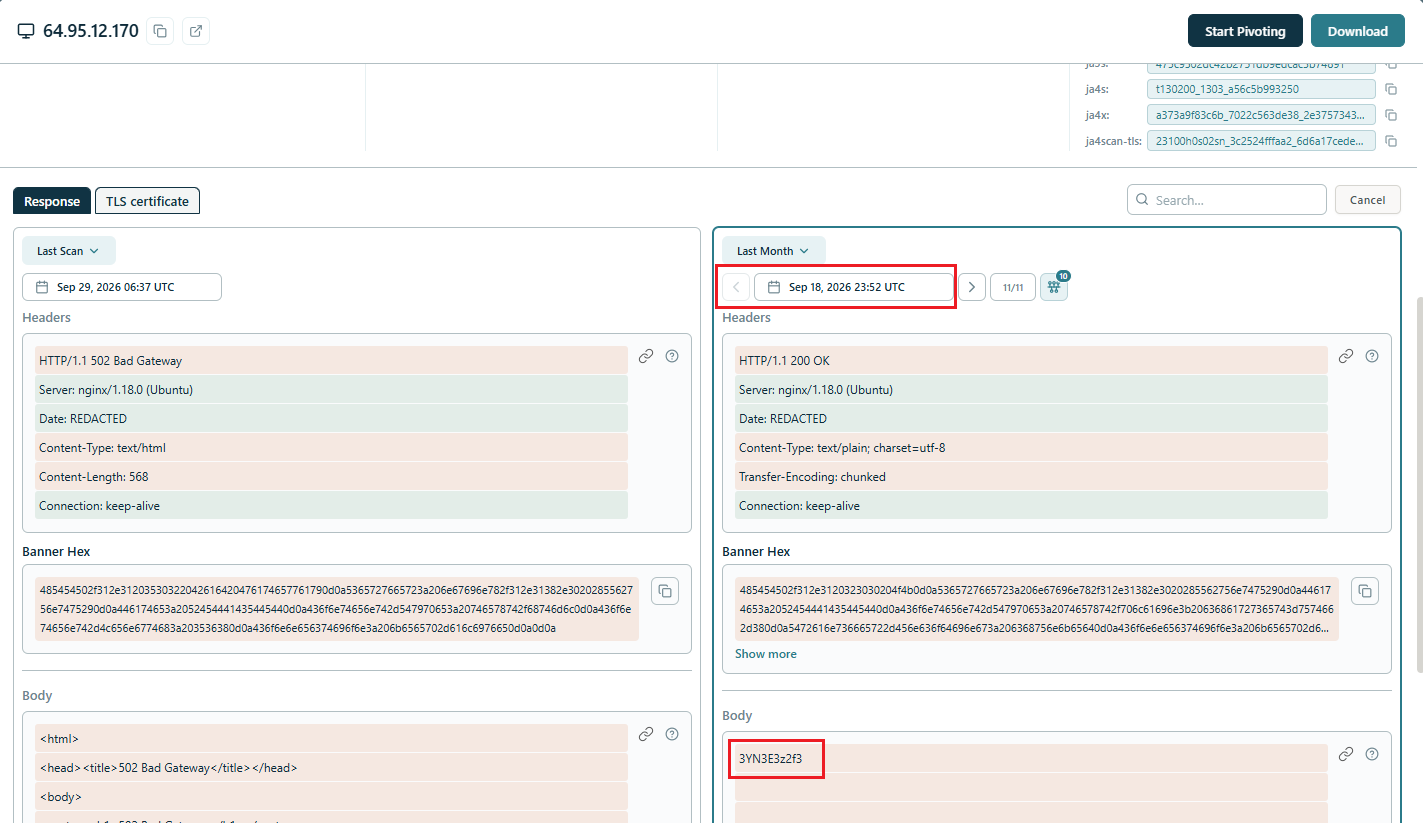 Modat Magnify revealed another MATCHBOIL host.
Beyond MATCHBOIL
While broadening the search query to identify more MATCHBOIL C2 servers, another suspicious host was found: 64.95.11[.]27/firefox-app-update[.]com. While this service did not reply with the same headers or HTTP content, some similarities were there: it was on the same ASN, had the same JA3s value, domain was registered via Hosting Concepts and the domain name was similar to the other identified UAC-0099 domains. Turns out this domain had already been connected to UAC-0099 back in 2024.
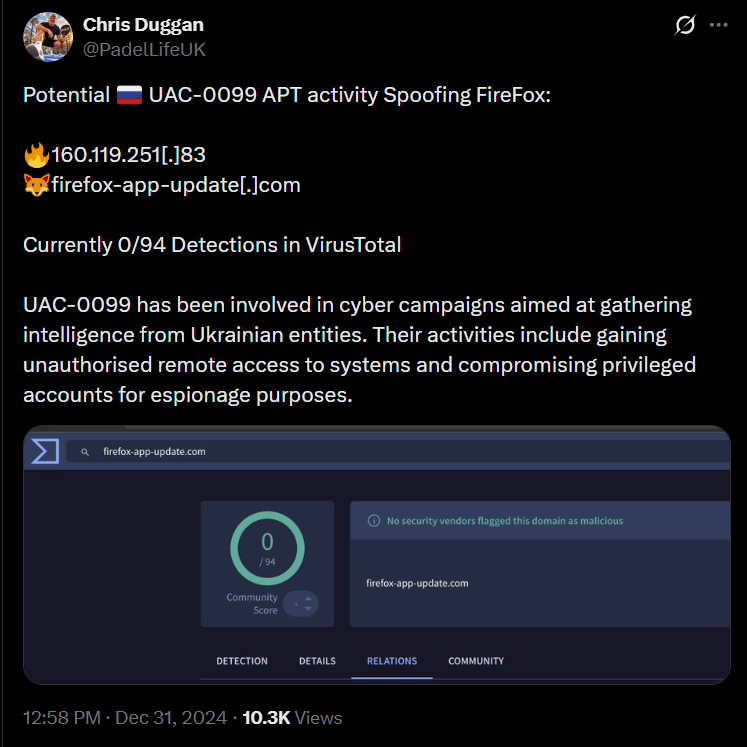 Blast from the past.
This prompted a broader look into similar hosts within the same ASN 399629. Some additional UAC-0099 hosts could be identified, some with lower confidence levels than others. This FOFA query was used to identify them, which also includes some false positive findings:
header="HTTP/1.1 404 Not Found" && header="Connection: close" && (header="Server: nginx/1.24.0 (Ubuntu)" || header="Server: nginx/1.18.0 (Ubuntu)") && asn="399629" && cert.issuer.org="Let's Encrypt" && (header="Content-Length: 14" || header="Content-Length: 0") && jarm!="27d40d40d00040d00042d43d000000d2e61cae37a985f75ecafb81b33ca523"
| IP | Domain | First seen | Confidence |
| 64.94.84[.]99 | white-check-security[.]tools | 2025-10-26 | High |
| 64.95.13[.]21 | virtualtelemetryassistant[.]com | 2025-12-12 | High |
| 64.95.10[.]28 | icore-hw-updatings[.]com | 2026-07-24 | Medium |
| 64.95.13[.]27 | files.korotuk[.]com | 2026-09-04 | Low |
| 64.94.85[.]156 | customs-kiev.com[.]ua | 2026-09-28 | High |
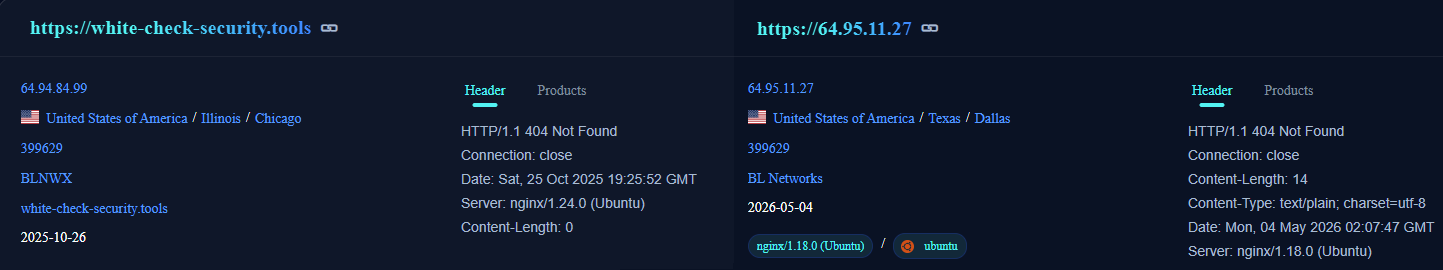 Highly likely UAC-0099 connected infrastructure.
These IP addresses hosted a varying set of services that had different fingerprints. Some responded with Content-Length: 0, while others with Content-Length: 14. Some services used nginx/1.18.0, while others nginx/1.24.0. The domains that were used had all been registered with either DevExpanse or Hosting Concepts (customs-kiev.com[.]ua was registered using Regery UA, DevExpanse is the operator for Regery). Most of these IP addresses and domain names already have a poor reputation on Virustotal, some with malicious files communicating with them. It is possible these hosts are C2 servers for a different malware or they were simply set up in a different way. However, not all of the hosts can be linked to UAC-0099 with high certainty, due to only finding circumstantial links and no smoking gun like the HTTP reply from the MATCHBOIL C2 servers.
Conclusion
The UAC-0099 infrastructure identified by ESET was analyzed, and infrastructure fingerprints were developed based on various identifying characteristics. In addition to discovering additional MATCHBOIL infrastructure, other UAC-0099 related infrastructure was also identified. All of the additional infrastructure was identified based on the threat actor’s repeated use of the same ASN and domain registrars, registering similar domain names and poorly configured C2 services. It would appear that OPSEC is not a priority for the group, at least as far as infrastructure goes.
UAC-0099 MATCHBOIL fingerprints (note these queries are based on the headers instead of the HTTP reply that was the clearest indicator):
FOFA: asn="399629" && header="Transfer-Encoding: chunked" && header="Content-Type: text/plain; charset=utf-8" && (header="Server: nginx/1.24.0 (Ubuntu)" || header="Server: nginx/1.18.0 (Ubuntu)") && header!="Cache-Control: no-store"
MODAT: same_service(port=443 protocol="http" transport="tcp" banner_hex=485454502f312e3120323030204f4b0d0a5365727665723a206e67696e782f312e31382e3020285562756e7475290d0a446174653a2052454441435445440d0a436f6e74656e742d547970653a20746578742f706c61696e3b20636861727365743d7574662d380d0a5472616e736665722d456e636f64696e673a206368756e6b65640d0a436f6e6e656374696f6e3a206b6565702d616c6976650d0a0d0a) asn=399629
Unknown UAC-0099 infrastructure fingerprint (note this is a broad query that also finds false positives):
FOFA: header="HTTP/1.1 404 Not Found" && header="Connection: close" && (header="Server: nginx/1.24.0 (Ubuntu)" || header="Server: nginx/1.18.0 (Ubuntu)") && asn="399629" && cert.issuer.org="Let's Encrypt" && (header="Content-Length: 14" || header="Content-Length: 0") && jarm!="27d40d40d00040d00042d43d000000d2e61cae37a985f75ecafb81b33ca523"
Initial indicators by ESET:
| Indicator | Description | First seen |
| virtualdailyplanner[.]pro | MATCHBOIL C2 | 2025‑11‑10 |
| telemetry-conf[.]com | MATCHBOIL C2 | 2025‑08‑12 |
| flycloud-service[.]com | MATCHBOIL C2 | 2026‑03‑03 |
| airarticlegenerate[.]com | MATCHBOIL C2 | 2025‑05‑07 |
| 64.95.10[.]223 | Host for flycloud-service[.]com | 2026‑03‑03 |
| 64.95.13[.]210 | Host for airarticlegenerate[.]com | 2025‑05‑07 |
Additional indicators:
| Indicator | Description | First seen | Confidence |
| 64.94.84[.]99 | Host for virtualdailyplanner[.]pro | 2025-11-10 | High |
| 64.95.12[.]130 | Host for telemetry-conf[.]com | 2025-08-14 | High |
| exchange-cab-center[.]com | MATCHBOIL C2 Domain | 2026-07-28 | High |
| 192.153.57[.]148 | Host for exchange-cab-center[.]com | 2026-07-28 | High |
| thunderbird-smp-extension[.]com | MATCHBOIL C2 Domain | 2026-06-19 | High |
| 64.94.85[.]94 | Host for thunderbird-smp-extension[.]com | 2026-06-19 | High |
| api-available-checker[.]com | MATCHBOIL C2 Domain | 2026-03-04 | High |
| 64.94.85[.]179 | Host for api-available-checker[.]com | 2026-03-04 | High |
| gold-kauf-limited[.]bar | MATCHBOIL C2 Domain | 2026-10-09 | High |
| 64.95.10[.]87 | Host for gold-kauf-limited[.]bar | 2026-10-09 | High |
| industriesbetbikeupdate[.]com | MATCHBOIL C2 Domain | 2026-09-24 | High |
| 64.95.11[.]193 | Host for industriesbetbikeupdate[.]com | 2026-09-24 | High |
| remote-fileviewer[.]com | MATCHBOIL C2 Domain | 2026-06-18 | High |
| 64.94.84[.]227 | Host for remote-fileviewer[.]com | 2026-06-18 | High |
| cloud-fileengine[.]com | MATCHBOIL C2 Domain | 2026-06-17 | High |
| 64.95.13[.]135 | Host for cloud-fileengine[.]com | 2026-06-17 | High |
| activation-planner[.]pro | MATCHBOIL C2 Domain | 2026-04-06 | High |
| 64.95.10[.]235 | Host for activation-planner[.]pro | 2026-04-06 | High |
| cache-extension-api-tool[.]icu | MATCHBOIL C2 Domain | 2026-08-31 | High |
| 64.95.12[.]170 | Host for cache-extension-api-tool[.]icu | 2026-08-31 | High |
| white-check-security[.]tools | UAC-0099 Infra | 2025-10-25 | High |
| 64.94.84[.]99 | Host for white-check-security[.]tools | 2025-10-25 | High |
| virtualtelemetryassistant[.]com | UAC-0099 Infra | 2025-08-28 | High |
| 64.95.13[.]21 | Host for virtualtelemetryassistant[.]com | 2025-08-28 | High |
| icore-hw-updatings[.]com | UAC-0099 | 2026-06-17 | Medium |
| 64.95.10[.]28 | Host for icore-hw-updatings[.]com | 2026-06-17 | Medium |
| customs-kiev.com[.]ua | UAC-0099 Infra | 2026-09-28 | High |
| 64.94.85[.]156 | Host for customs-kiev.com[.]ua | 2026-09-28 | High |